Overview Integrate OneFirewall Alliance (OFA) threat feeds with ForcePoint NGFW using Security Management Center (SMC) and External Dynamic Feeds. This enables real-time policy enforcement based on live threat data for:
Malicious IPs
Malicious URLs
Compatibility Compatible with ForcePoint NGFW Software 7.0, 6.11, 6.10, 6.9, 6.8, 6.7, 6.5, managed through Security Management Center (SMC).
Prerequisites
A valid OneFirewall Alliance account.
ForcePoint running 6.5 or later (7.0 recommended).
Console access.
Internet access from the gateway to OneFirewall’s feed URLs.
HTTPS inspection must allow outbound connections to threat feed URLs, if required by policy.
Step 1: Generate API Token
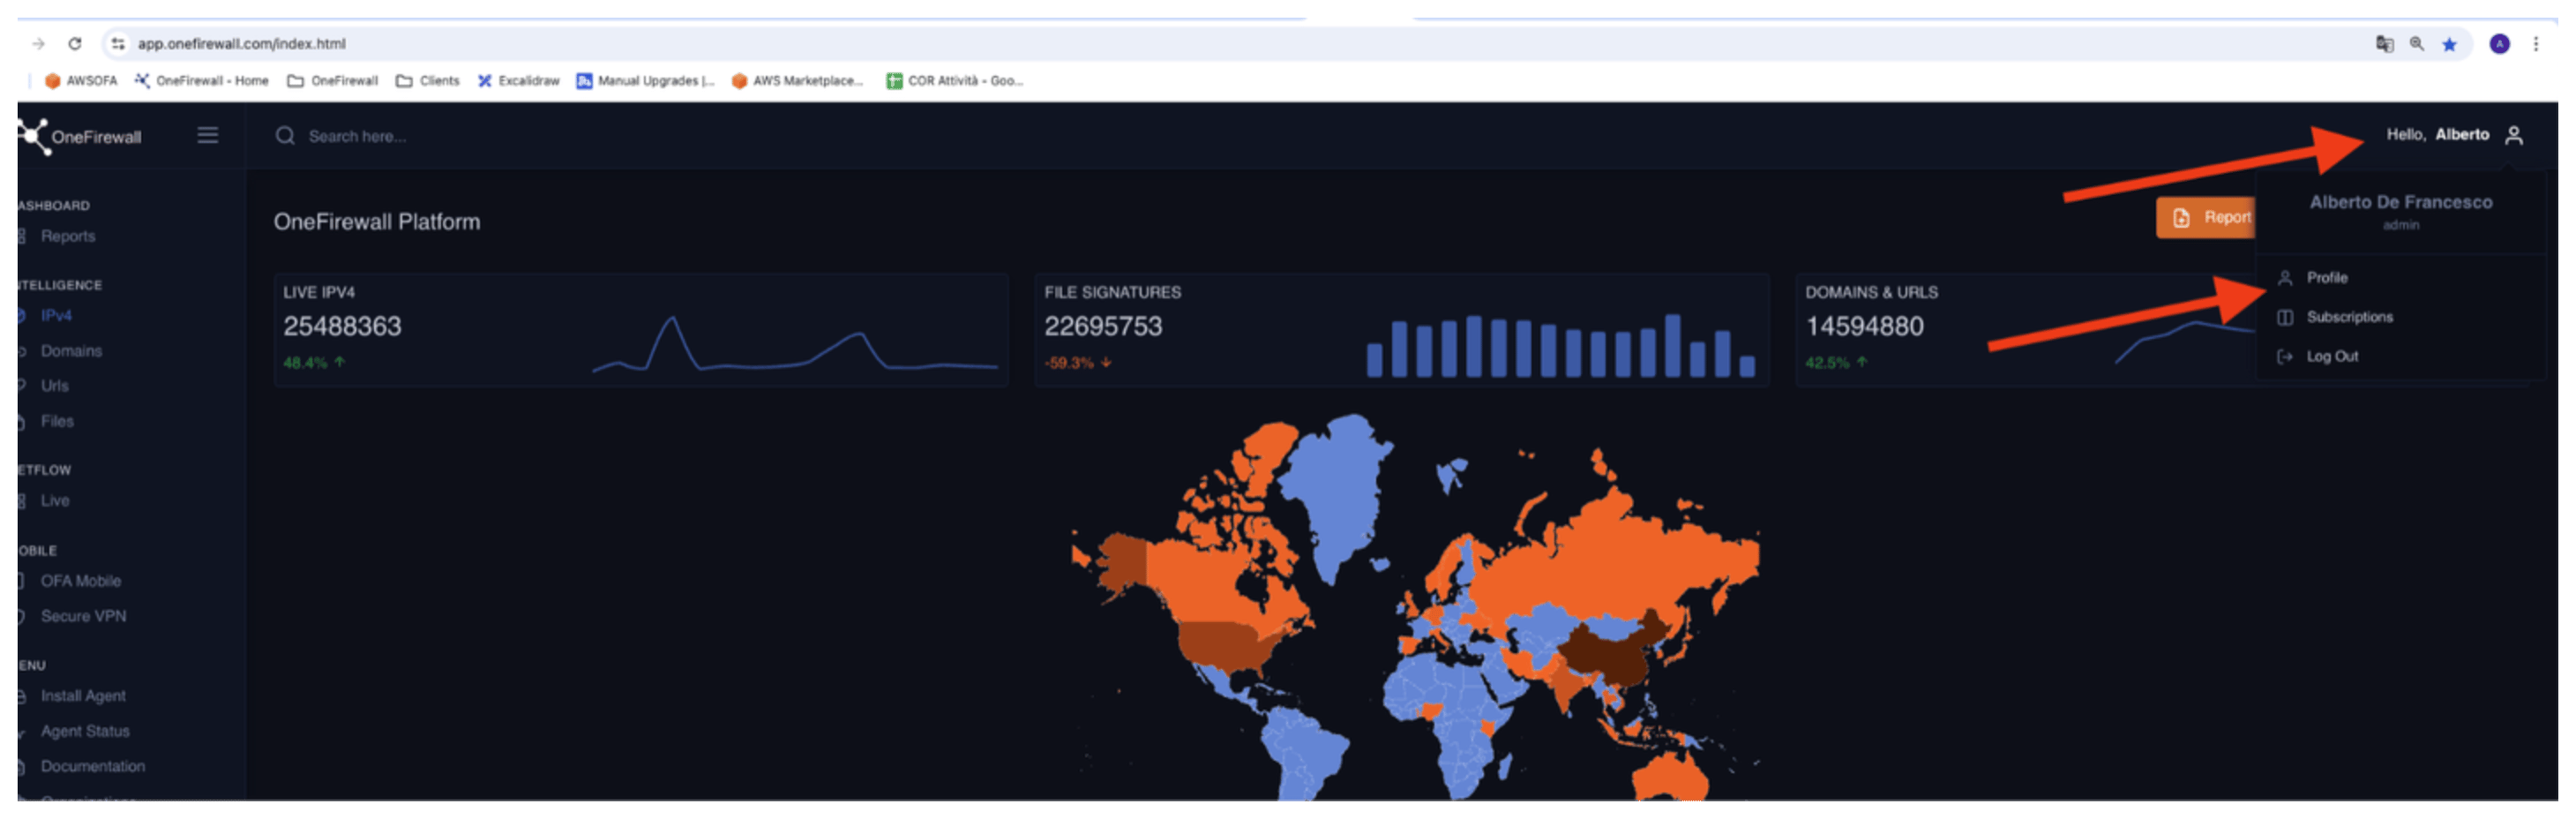
Log into your OneFirewall Alliance dashboard.
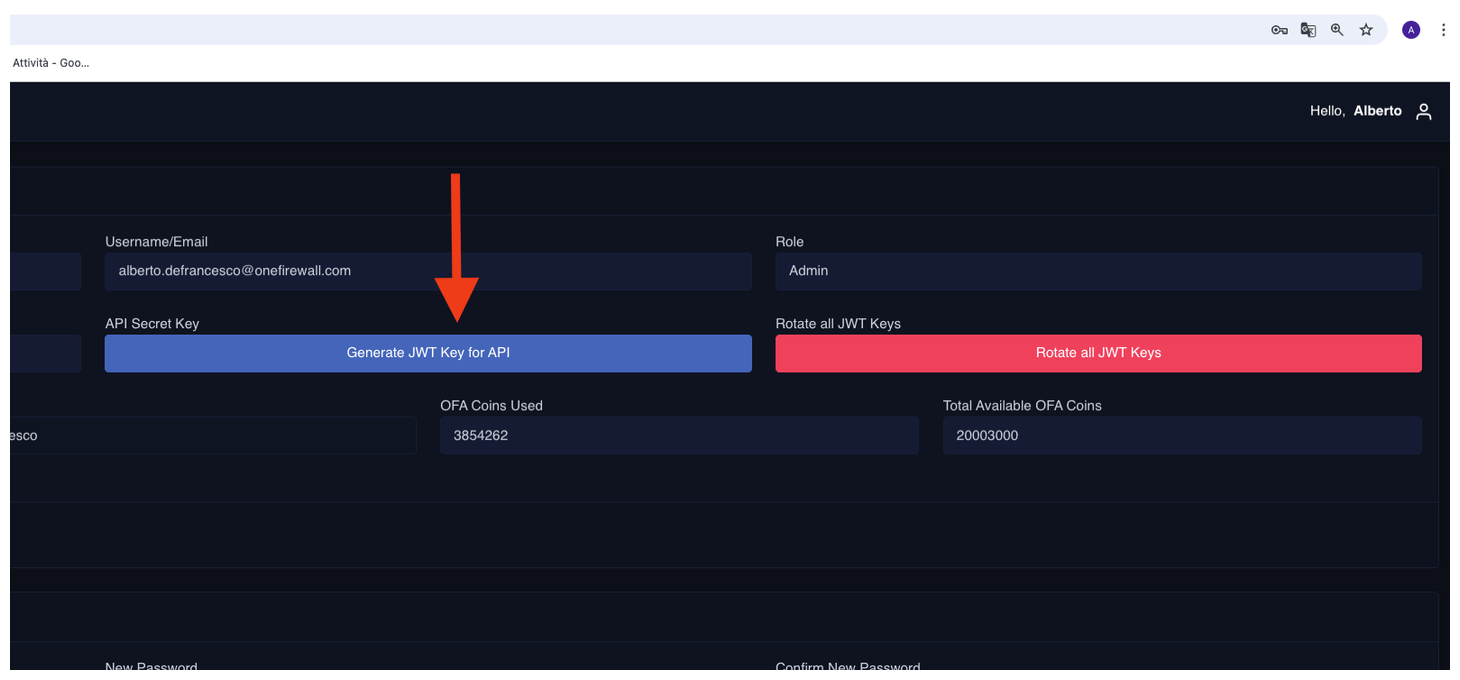
Go to the API Access section.
Click Generate JWT Token .
Save the token securely — it authenticates feed requests.
Install Docker and Docker Compose Prepare your deployment directory
Download the WCF Agent Docker image into this folder.
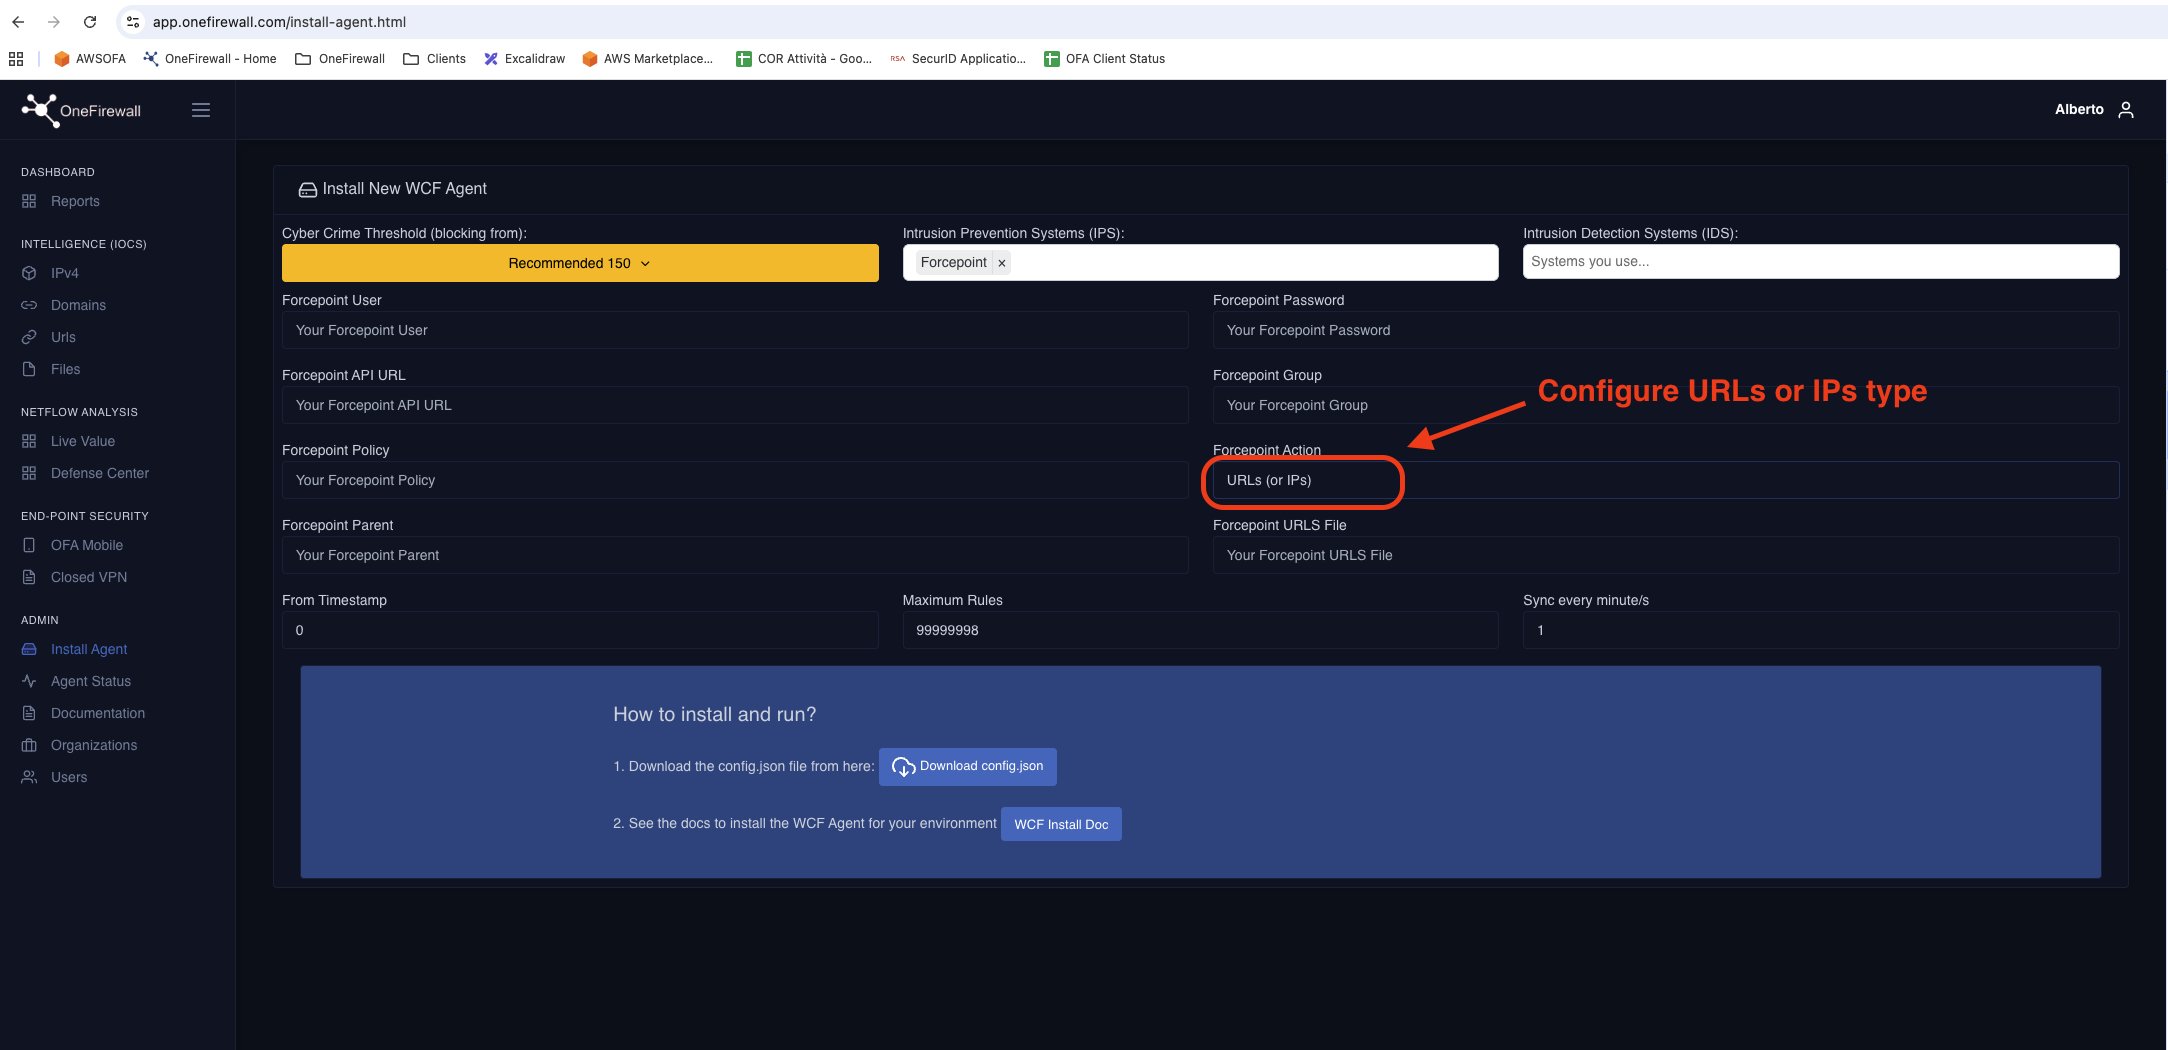
Obtain your config.json from OneFirewall’s Install Agent page.
Place config.json in ~/wcf-agent/onefirewall/config.
Create docker-compose.yml
Contact the OneFirewall support team for access to download the WCF Agent binary image.
Launch the agent Notes
OneFirewall uses JWT-based Bearer Authentication.
Feeds refresh automatically and are optimized for ForcePoint NGFW SMC 7.0 integration.
All feed types can be used simultaneously, in different rules or combined policies.